

Key Takeaways:
SNMPv1 and SNMPv2c should be treated as legacy security risks. Both versions transmit community strings and management data without encryption, allowing anyone able to observe the traffic to potentially recover credentials and enumerate device information. CISA recommends using SNMPv3 as the only deployed SNMP version because it supports authentication and payload encryption.
An exposed SNMP agent can reveal far more than device health. Valid SNMP access may expose interface and routing information, ARP data, system details, installed software, configuration context, and other intelligence attackers can use to map internal networks and prioritize targets.
Default or reused community strings turn a single weakness into broad access. “public” and “private” remain commonly tested values; shared strings also eliminate meaningful device-by-device accountability and make one disclosed credential useful across multiple systems. Read-write SNMP access is particularly dangerous because it can enable management-plane changes, not merely information disclosure.
SNMPv3 reduces risk only when configured securely. Use authenticated and encrypted SNMPv3 – prefer modern SHA-based authentication and AES privacy along with unique device credentials, least-privilege views, and source-IP restrictions. SNMPv3’s User-based Security Model was specifically designed to introduce per-user security controls for the protocol.
SNMP belongs in continuous exposure management and penetration testing. Inventory every SNMP-enabled asset, eliminate unnecessary agents, block UDP 161/162 at the perimeter, isolate required management traffic to dedicated management networks, monitor for unauthorized queries or brute forcing, and patch vulnerable implementations. Protocol security alone does not prevent exploitable vendor flaws; for example, Cisco’s 2025 advisory for CVE-2025-20352 describes a crafted SNMP-packet attack path against affected IOS/IOS XE devices.
What is Simple Network Management Protocol (SNMP)?
Simple Network Management Protocol (SNMP) is one of the oldest and most widely deployed protocols for monitoring and managing network devices. It allows administrators to query routers, switches, firewalls, servers, printers, and other networked equipment for performance data, configuration details, and operational status. SNMP operates over UDP (typically ports 161 and 162) and uses a manager-agent model where a central management station polls agents running on network devices.
The problem is that SNMP was designed in 1988 for functionality, not security. The earliest versions transmit everything in cleartext, including the community strings that serve as the only form of authentication. That means anyone with network access can intercept SNMP traffic and extract credentials, device configurations, routing tables, ARP caches, and installed software inventories (this brings back memories from the good ol’ days). For attackers, an exposed SNMP service is one of the fastest ways to map an entire network and identify high-value targets. It’s also one of the most commonly exposed services on the internet.
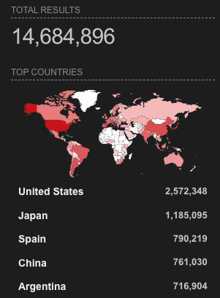
(From shodan.io)
Differences Between SNMP v1 vs v2 vs v3
The security gap between SNMP versions is significant, and understanding these differences is critical for assessing your exposure. SNMPv1 and v2c rely entirely on community strings transmitted in plaintext. SNMPv3 introduced authentication and encryption, but adoption remains inconsistent across enterprise environments.
| Feature | SNMPv1 | SNMPv2c | SNMPv3 |
|---|---|---|---|
| Authentication | Community string (plaintext) | Community string (plaintext) | Username + password (HMAC-MD5/SHA) |
| Encryption | None | None | DES, AES-128, AES-256 |
| Access Control | None built-in | None built-in | User-based Security Model (USM) |
| Message Integrity | None | None | HMAC-based verification |
| Community Strings | Sent in cleartext | Sent in cleartext | Eliminated entirely |
| Risk Level | Critical | Critical | Low |
Security recommendation: Disable SNMPv1 and SNMPv2c where possible. Use SNMPv3 with SHA authentication and AES privacy, unique per-device credentials, least-privilege views, and management-network access restrictions.
Despite SNMPv3 being available since 2004, a large number of organizations still run v1 or v2c in production. Legacy devices, vendor defaults, and the complexity of migrating to SNMPv3 all contribute to this. Every device still running v1 or v2c is transmitting credentials in the clear and is vulnerable to interception, enumeration, and unauthorized access. Identifying those devices can easily be done here.
What are SNMP Vulnerabilities?
SNMP vulnerabilities fall into two main categories. The first is protocol-level weakness like the inherent lack of authentication and encryption in v1 and v2c. The second is implementation-level, where vendors ship devices with insecure SNMP defaults, buggy agent code, or misconfigured access controls.
What makes SNMP vulnerabilities particularly dangerous is the depth of access they provide. A compromised SNMP service does not just leak a device’s status. With write access (using the default “private” community string that many devices still ship with), an attacker can modify device configurations, change routing tables, disable security features, and pivot deeper into the network. SNMP is often overlooked during penetration tests because it is treated as a monitoring protocol rather than an attack surface.
SNMP Vulnerabilities vs Other Network Protocol Vulnerabilities
Unlike vulnerabilities in protocols like HTTP or SSH, SNMP vulnerabilities are often invisible to standard security monitoring. SNMP traffic on UDP 161/162 is rarely inspected by web application firewalls or intrusion detection systems tuned for TCP-based attacks, and most SIEM platforms do not alert on SNMP enumeration activity by default.
The reason is that SNMP enumeration is inherently quiet traffic. It uses UDP port 161, which most network security stacks treat as legitimate management activity. SNMP queries look identical to normal monitoring traffic from tools like SolarWinds, PRTG, or Nagios. Most SIEM vendors ship their default rulesets focused on authentication events, privilege escalation, malware signatures, and lateral movement rather than management protocol enumeration. Default content packs for Splunk, Microsoft Sentinel, IBM QRadar, and Elastic SIEM do not include SNMP enumeration detection rules out of the box. Organizations would need to build custom correlation rules, and most do not know they need to.
SNMP also provides a unique combination of reconnaissance and exploitation capability in a single protocol. Other attack vectors typically require multiple stages and tools to achieve what a single SNMP query can deliver. One successful GET request with valid community strings can return an entire device inventory, while a SET request can alter a device’s configuration in real time. That combination of passive intelligence gathering and active device manipulation in one protocol, over one port, with no authentication beyond a plaintext string, is what makes SNMP exposure fundamentally different from other network protocol vulnerabilities.
Common Locations for SNMP Attacks
SNMP agents run on nearly every category of network-connected hardware. Attackers target these devices because they are often deployed with default configurations and rarely receive the same security attention as servers or workstations.
Routers, Switches, and Firewalls
Network infrastructure devices are the highest-value targets for SNMP attacks. Routers and switches with exposed SNMP services leak routing tables, VLAN configurations, ARP caches, and interface statistics. Firewalls with SNMP enabled can expose rule sets, NAT configurations, and VPN tunnel details. Compromising SNMP on these devices gives an attacker a map of the entire network architecture and the ability to modify traffic flow if write access is available.
Edge and IoT Devices
IoT devices, industrial control systems, building automation controllers, and edge computing appliances frequently run SNMP agents with factory-default community strings. These devices are often deployed outside the visibility of central IT security teams. Many IoT manufacturers implement only SNMPv1 with no option to upgrade, creating permanent exposure that persists for the lifetime of the device.
Printers, UPS Systems, and Other Network Equipment
Network-attached printers, uninterruptible power supplies, HVAC controllers, VoIP phone systems, storage appliances, and medical devices all commonly ship with SNMP enabled by default. These devices are rarely included in vulnerability management programs and frequently retain default community strings for years. Attackers use them as pivot points to access network segments that would otherwise require authenticated access.
Common SNMP Exploits
Default Community Strings
The most common SNMP exploit requires zero sophistication. Manufacturers ship devices with community strings set to “public” for read access and “private” for write access. These defaults are documented in every product manual and compiled into every penetration testing wordlist. An attacker who discovers an SNMP service simply tries the defaults first, and the success rate is unusually high. During Netragard’s network penetration testing engagements, we often find production infrastructure running with the default community strings still set.
Misconfiguration and Unauthenticated Access Risks
Beyond default strings, SNMP misconfigurations include exposing SNMP services to the internet when they should be restricted to management VLANs, enabling write access when only read is needed, using the same community string across all devices, and failing to implement IP-based access control lists. Each of these misconfigurations compounds the impact of a successful attack because they eliminate independent layers of defense that would otherwise contain the damage.
In SNMPv1 and v2c, there is no mechanism to verify the identity of the requesting party beyond the community string itself. If the string is correct, access is granted regardless of source. This means a single leaked or guessed community string can unlock read or write access to every device sharing that string. Systems running SNMPv1 are found in abundance with internet connectable configurations.
Remote Code Execution (RCE)
SNMP agent implementations have a history of buffer overflow and memory corruption vulnerabilities that lead to remote code execution. These flaws exist in the code that parses SNMP requests, and a specially crafted packet can crash the agent process or allow an attacker to execute arbitrary commands on the underlying operating system. CVE-2025-68615, a critical vulnerability in Net-SNMP’s snmptrapd service (CVSS 9.8), demonstrates that this class of vulnerability is not historical. It requires no authentication, no user interaction, and is exploitable over the network against any exposed snmptrapd instance.
Denial of Service (DoS)
SNMP services can be weaponized for denial-of-service attacks in two ways. First, vulnerable SNMP agents can be crashed by malformed packets, taking critical network infrastructure offline. Second, SNMP amplification attacks exploit the protocol’s UDP-based communication to generate large responses from small requests. Attackers send spoofed SNMP queries with the victim’s source IP address, and the SNMP agent sends a much larger response to the victim. SNMP amplification has been used in some of the largest DDoS attacks ever recorded.
How Attackers Discover SNMP Vulnerabilities
Attackers discover SNMP services through the same techniques that Netragard replicates during penetration testing engagements. The process starts with network sweeps. Port scanning tools like Nmap probe against UDP 161 and 162 across target ranges to identify live SNMP agents. Because SNMP runs on UDP, these scans are often missed by network monitoring that focuses on TCP connections.
Once an SNMP service is found, the attacker attempts community string guessing using wordlists that include defaults like “public,” “private,” the organization’s name, and common variations. Tools like onesixtyone and snmpbrute can test thousands of strings in seconds.
After obtaining valid credentials, attackers use SNMP enumeration tools (snmpwalk, snmpbulkwalk, snmp-check) to extract as much information as possible. MIB (Management Information Base) walking reveals system descriptions, network interfaces, routing tables, running processes, installed software, user accounts, and storage details. This intelligence feeds directly into the next stages of an attack, whether that is lateral movement, privilege escalation, or data exfiltration.
At Netragard, we take this further by testing SNMP write access to determine whether an attacker could modify device configurations, alter routing behavior, or disable logging. This is inherently risky testing. A single SET request to the wrong OID on a production device can change a routing table, disable an interface, or wipe a configuration.
Automated scanners either skip write-access testing entirely because they cannot assess those consequences, or they run it blindly and risk disrupting production infrastructure. Human testers evaluate each target in context, understand what the device does in the environment, and make judgment calls about what to test safely and how far to push. That judgment is why human testers evaluate each target in context, understand what the device does in the environment, and make judgment calls about what to test safely and how far to push. That judgment is why human penetration testing is essential for identifying SNMP risks that automated tools cannot safely assess.
Examples of Real-World SNMP-Based Attacks
Cisco IOS/IOS XE SNMP Zero-Day (2025). In 2025, attackers exploited CVE-2025-20352, a stack overflow vulnerability in Cisco’s SNMP implementation affecting both IOS and IOS XE platforms. The attackers used valid SNMP community strings to trigger the overflow and deploy Linux-based rootkits on compromised switches, achieving persistent remote code execution as root. The campaign, tracked as Operation Zero Disco by Trend Micro, targeted older switches that had not been patched, but the vulnerability affected current firmware versions as well. NIST National Vulnerability Database entry: https://nvd.nist.gov/vuln/detail/CVE-2025-20352
Net-SNMP snmptrapd Buffer Overflow (2025). CVE-2025-68615 exposed a critical buffer overflow in the Net-SNMP snmptrapd daemon, which is deployed across millions of Linux and Unix systems for SNMP trap processing. With a CVSS score of 9.8, this vulnerability allows unauthenticated remote attackers to crash the daemon or execute arbitrary code. No authentication is required and the attack vector is entirely network-based. NIST National Vulnerability Database entry: https://nvd.nist.gov/vuln/detail/CVE-2025-68615
Cisco FirePOWER SNMP Default Credentials (2022). CVE-2022-20918 revealed that Cisco FirePOWER and Firepower Management Center software shipped with default SNMP credentials for v1 and v2c. Unauthenticated remote attackers could perform SNMP GET requests using these defaults to extract sensitive device information from security appliances, the very devices organizations rely on to protect their networks. NIST National Vulnerability Database entry: https://nvd.nist.gov/vuln/detail/CVE-2022-20918
Mirai Botnet SNMP Exploitation (2016–2017). The Mirai botnet compromised hundreds of thousands of IoT devices using default credentials, including SNMP community strings. Infected devices were weaponized for massive DDoS attacks, including the Dyn DNS attack that took down major internet services. The financial impact ran into hundreds of millions of dollars. Mirai demonstrated that SNMP defaults on IoT devices are not just a theoretical risk but a weapon that can disrupt critical internet infrastructure.
How To Protect Against SNMP-Related Risks
1. Review and Update SNMP Configurations
Start with a complete inventory of every device running SNMP in your environment. Many organizations do not know how many SNMP-enabled devices they have because SNMP is often enabled by default at deployment and then forgotten. Audit each device for its SNMP version, community strings, access level (read vs. read-write), and network exposure. Disable SNMP entirely on any device where it is not operationally required.
2. Use Secure Versions of SNMP
Migrate all devices to SNMPv3 with authentication (SHA-256 or SHA-512) and encryption (AES-256). Disable v1 and v2c completely on every device that supports v3. For legacy devices that only support v1 or v2c, implement compensating controls by restricting SNMP access to specific management stations via access control lists and isolating the devices on dedicated management VLANs with no direct internet exposure.
3. Change Default Strings
Replace all default community strings with long, complex values unique to each device or device group. Treat community strings with the same rigor as administrative passwords. Do not reuse community strings across different security zones or device categories. Rotate community strings on a regular schedule and immediately after any personnel change involving network operations staff.
4. Implement Access Control Lists
Configure access control lists (ACLs) on every SNMP-enabled device to restrict which IP addresses can communicate with the SNMP agent. Limit SNMP access to your dedicated network management stations. Block SNMP traffic (UDP 161/162) at perimeter firewalls to prevent external SNMP enumeration. Implement internal network segmentation to restrict SNMP traffic to management VLANs.
5. Monitor and Audit
Configure your SIEM and network monitoring tools to alert on SNMP enumeration activity, community string brute force attempts, and SNMP traffic from unauthorized sources. Log all SNMP access attempts and review logs regularly. Establish baselines for normal SNMP traffic patterns so that anomalous activity is detectable. Many SNMP-based attacks succeed because no one is watching SNMP traffic at all.
Is SNMP Still Safe to Use?
SNMPv3 with proper authentication and encryption is safe for network management when configured correctly. The protocol itself is mature, well-understood, and supported by virtually every network device manufacturer. The risk does not come from the protocol. It comes from running outdated versions with plaintext authentication, using default community strings, and exposing SNMP services to networks where they should never be accessible.
If your organization still runs SNMPv1 or v2c in production, those services are not safe. They are actively targeted by attackers and automated scanning tools. The question is not whether they will be discovered but when. Every month that passes with default community strings on internet-facing or insufficiently segmented devices is a month of unnecessary exposure.
How Can Organizations Assess SNMP Exposure?
Assessing SNMP exposure starts with internal and external network scanning to identify every device running an SNMP agent. Automated vulnerability scanners will flag default community strings and outdated SNMP versions, but they cannot accurately or safely assess the real-world impact of SNMP exposure on your specific environment. A scanner will tell you that a device has “public” as its community string. It will not tell you that an attacker can use that access to extract your routing table, identify your internal network segmentation, and pivot to a database server three hops away.
This is where manual penetration testing becomes essential. A skilled tester will enumerate SNMP services, extract actionable intelligence from MIB data, test write access, and demonstrate the full attack chain that an adversary would execute. That level of assessment requires expertise that automated tools cannot replicate.
Why Manual Penetration Testing Is Important for Hardening SNMP
Automated scanners check whether SNMP is running and whether default community strings are present. That is necessary but insufficient. Manual penetration testing evaluates what an attacker can actually do with SNMP access in the context of your environment.
During a manual penetration testing engagement, a tester uses SNMP enumeration data the same way an attacker would. They map the network topology from routing tables, identify high-value targets from device inventories, extract user accounts from host MIBs, and chain SNMP findings with other vulnerabilities to demonstrate realistic attack paths. An automated scanner cannot do this because it does not understand the relationship between an SNMP finding on a switch and a misconfigured database server two segments away.
Manual penetration testing also identifies SNMP services that automated tools miss. Devices running SNMP on non-standard ports, SNMP agents that respond only to specific community strings not in default wordlists, and SNMP services hidden behind NAT or load balancers all require manual discovery techniques. Red teaming services take this even further by testing whether SNMP-based attack paths can bypass your detection and response capabilities.
How Netragard Can Help Protect Against SNMP Vulnerabilities
Netragard has been delivering expert penetration testing since 2006. Our team conducts thorough network penetration testing that includes comprehensive SNMP enumeration, community string testing, write-access verification, and full attack chain demonstration. We do not just flag that SNMP is running with default credentials. We show you exactly what an attacker can access, what they can modify, and how they can use SNMP as a pivot point to reach your most sensitive systems.
Our Real Time Dynamic Testing™ (RTDT) methodology adapts to what we discover during the engagement, including SNMP findings that automated tools would report as isolated low-severity issues but that actually represent critical paths to compromise. We deliver contextualized threat intelligence that maps SNMP vulnerabilities to realistic attack scenarios specific to your environment.
Request a Quote to find out how Netragard can help you identify and eliminate SNMP vulnerabilities before an attacker exploits them.
FAQ
What is the biggest security risk with SNMP?
The biggest risk is running SNMPv1 or v2c with default community strings. These versions transmit authentication credentials in plaintext, and the factory defaults (“public” and “private”) are universally known. An attacker who discovers an exposed SNMP service with default strings can immediately enumerate the device’s configuration, network topology, and in many cases modify settings with write access.
Can attackers use SNMP to take control of network devices?
Yes. If an attacker has write access via SNMP (using the read-write community string), they can modify device configurations, change routing tables, disable security features, and alter firewall rules. In cases where SNMP agent implementations contain buffer overflow vulnerabilities, attackers can achieve remote code execution and take complete control of the underlying operating system.
Is upgrading to SNMPv3 enough to secure my network?
SNMPv3 with authentication and encryption is significantly more secure than v1 or v2c, but it is not a complete solution by itself. SNMPv3 must be configured with strong authentication protocols (SHA-256 or higher), robust encryption (AES-256), unique credentials per device, and proper access control lists. A poorly configured SNMPv3 deployment can still be vulnerable.
How often should organizations test for SNMP vulnerabilities?
SNMP configurations should be tested at least annually as part of a comprehensive penetration testing program, and immediately after any significant network changes such as new device deployments, firmware upgrades, or network architecture modifications. Continuous monitoring for unauthorized SNMP services should run between testing cycles.
Why do automated scanners miss critical SNMP vulnerabilities?
Automated scanners check for known default community strings and version information, but they cannot assess the contextual impact of SNMP findings. They do not chain SNMP data with other vulnerabilities, they miss non-standard configurations, and they cannot demonstrate realistic attack paths. Manual penetration testing fills this gap by evaluating SNMP exposure the way an actual attacker would exploit it.